Book Appointment Now
PKI infrastructure CA/RA/VA
1. Certificate Authority ( CA )
Jrsys can build a CA for enterprise or organization to apply certificate to achieve electronic application, such as: e-document signature, e-supply chain system, e-procurement system, e-commerce, or email encryption, etc. Governmental entities can build their own CA for temporary certificate issuance or internal data encryption exchange. Government agencies can build their own CA for temporary certificate issuance or internal data encryption exchange. Through the issuance of certificates, various application systems can strengthen their security level.
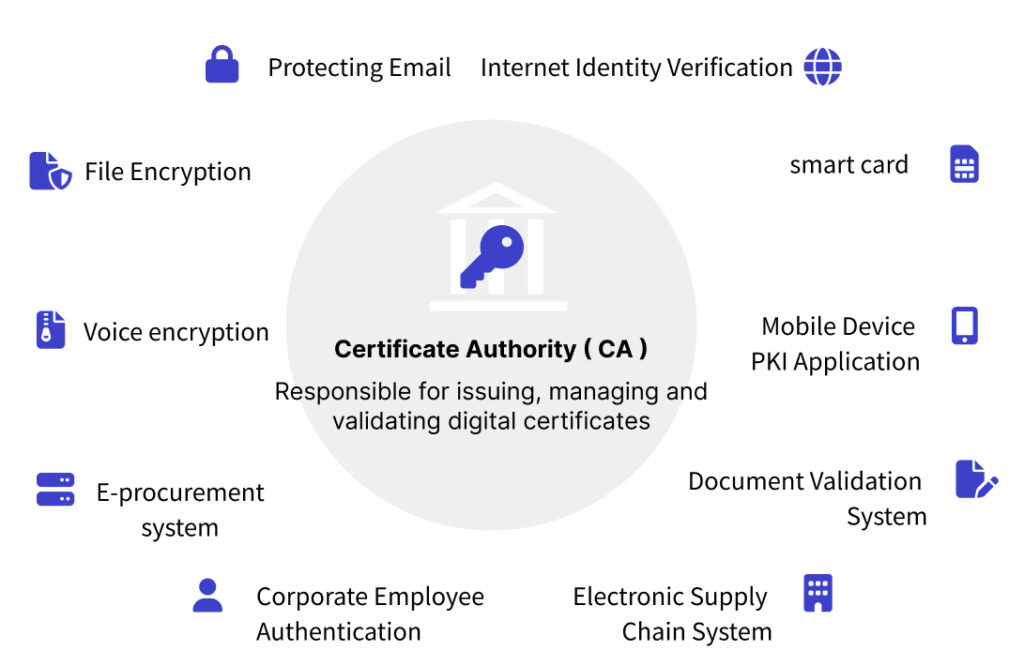
Certification Authority(CA) is an entity that issues digital certificates. The digital certificate certifies the ownership of a public key by the named subject of the certificate. This allows others (relying parties) to rely upon signatures or assertions made by the private key that corresponds to the public key that is certified. In this model of trust relationships, a CA is a trusted third party that is trusted by both the subject (owner) of the certificate and the party relying upon the certificate. CAs are characteristic of many public key infrastructure (PKI) schemes. We can assist the entity that wants to issue commercial CAs, or some providers issue digital certificates to the public. The primary points of industry and business regarding digital signatures has been to prevent conflicting and overly burdensome local regulation and to establish that electronic writings satisfy the traditional requirements associated with paper documents. Further our partners who use E-Sign, E-provision chain, E-consumption, and E-commerce would be ensured that: a signature, contract or other record relating to such transaction may not be denied legal effect, validity, or enforceability solely because it is in electronic form; and a contract relating to such transaction may not be denied legal effect, validity or enforceability solely because an electronic signature or electronic record.
Features
Easy Installation by Web Interface
- Tutoring by web interface to build up Certificate Authority. No complicated installation and technical message.
Highly Secure Key by Supporting 2048 bits
- The key of signing certificate would be settle down by system. The shorter length of key is NOT allowed.
Restore and Management
- The log has been backup for fully recovery. Support HSM
Systematic Infrastructure
- Support Multi-layer CA infrastrue
- Meet the requirement of large scale commercial CA
2. Registration Authority ( RA )
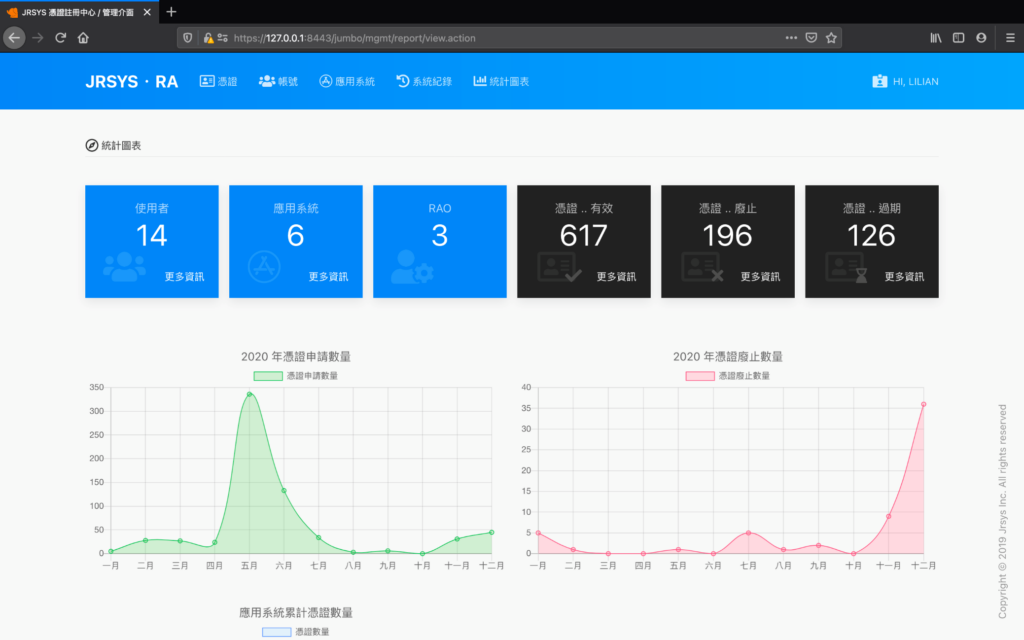
JRSYS Registration Authority (RA) establishes a credential application window, provides a web-based management method for the Registration Administrator (RAO), and reduces the procedures for users to install software. The CA makes a request to issue a certificate and obtains a digital certificate for the user.
The Registration Authority (RA) provides hierarchical authorization management of enterprise organizations. The system administrator can authorize the credential registration function to the personnel in the unit. The unit administrator fills in the user information and uploads the relevant authentication information, and checks the real identity of the user, to ensure the correlation between the certificate applicant’s information and the certificate, and the certificate registration administrator (RAO) will make a certificate application for the user after checking the user’s information is correct.
The Registration Authority (RA) provides hierarchical authorization management of enterprise organizations. The system administrator can authorize the credential registration function to the personnel in the unit. The unit administrator fills in the user information and uploads the relevant authentication information, and checks the real identity of the user, to ensure the correlation between the certificate applicant’s information and the certificate, and the certificate registration administrator (RAO) will make a certificate application for the user after checking the user’s information is correct.
Jrsys registration authority (RA) system provides Web base front end service for the RAO (Registration Authority Operator) to verify the user then the RA sends Certificate Signing Request to CA to issue digital certificate.
儀錶板 Dashboard
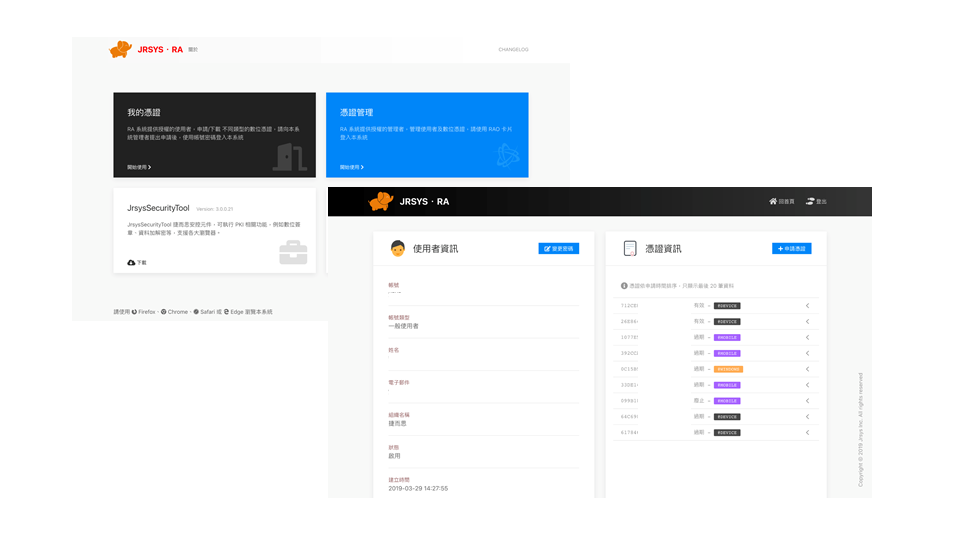
使用者申請憑證
Features
- User friendly registration user interface with graphic audit report.
- Easy to manage in daily operation.
- Support multiple CAs that follow the standard PKCS#10
- Certificate Signing Request (CSR)
- Support worldwide famous smart card tokens with RSA PKCS#11/ MS CAPI.
- Support Jrsys FIPS 140-2 Level 3 Mobile Slim SIM sticker and CC EAL5+ Secure MicroSD card.
- Provide standard RA functions such as: certificate status check, certificate application, certificate revocation, certificate suspended, certificate renew functions
- Provide audit records of the RA system, such as login, issue certificate, reset smart card PIN code.
- Fully integrated with Jrsys 3A Secure Single Sign On system
Supported Databases
- PostgreSQL
- Oracle® 9i, 10g and 11g
- Microsoft SQL Server™ MySQL
- DB2
- Sybase
3. Validation Authority ( VA )
JRSYS Registration Authority (RA) establishes a credential application window, provides a web-based management method for the Registration Administrator (RAO), and reduces the procedures for users to install software. The CA makes a request to issue a certificate and obtains a digital certificate for the user.
The Registration Authority (RA) provides hierarchical authorization management of enterprise organizations. The system administrator can authorize the credential registration function to the personnel in the unit. The unit administrator fills in the user information and uploads the relevant authentication information, and checks the real identity of the user, to ensure the correlation between the certificate applicant’s information and the certificate, and the certificate registration administrator (RAO) will make a certificate application for the user after checking the user’s information is correct.
Jrsys registration authority (RA) system provides Web base front end service for the RAO (Registration Authority Operator) to verify the user then the RA sends Certificate Signing Request to CA to issue digital certificate.
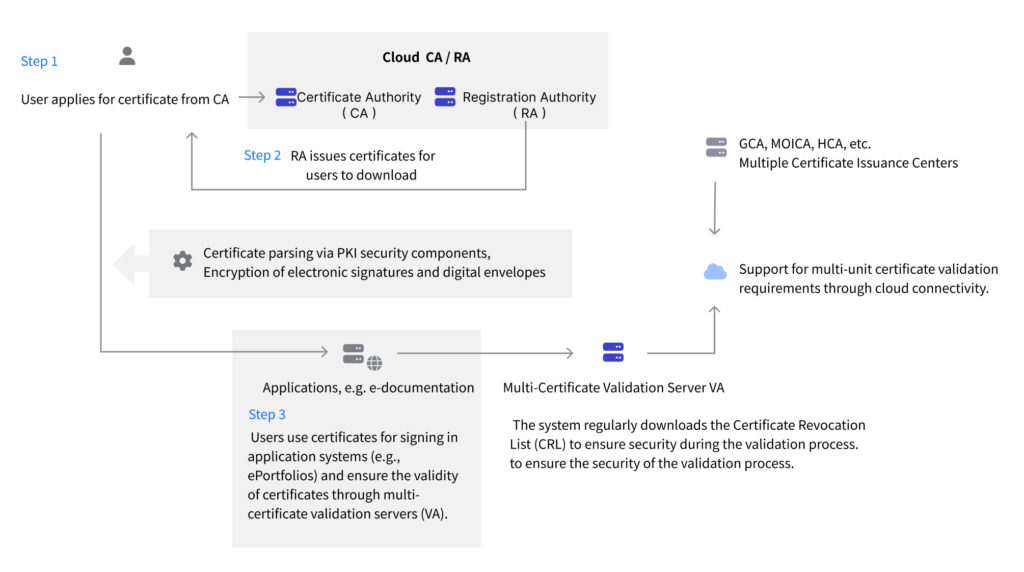
Jrsys Mobile Security Validation Service is an industry standards-based, real-time certificate status checking solution that ensures the revoked or invalid credentials cannot be used for secure transactions, smart card login, network access and helps to alleviate deployment and performance concerns associated with certificate revocation lists (CRL). Our scalable Validation Authority supports certificates issued by most of the public Certificate Authority (CA), as well as other third-party private CA, such as Microsoft Windows CA.
Jrsys Mobile Security Validation Service provides high performance, cost-effective scalability to help organizations perform real-time transactions and failover protection so processes may continue without interruption. All of the digital signature logs will be stored in Jrsys VA as the audit logs, Organization can verify these logs anytime if she wants.
Features
- Distributed certificate validation infrastructure which provides high performance, high availability server for responding to PKI digital certificate validation requests of PKI-enabled application.
- Secure SSL/TLS communication with VA Server and ability to sign validation responses.
- Source IP filtering for all application that connect to VA.
- Automatic periodically downloading and updating multiple Certificate Revocation List (CRL) from CA
- Supports FIPS 140-2 Level 3 or above Hardware Security Module (HSM)
- Support Jrsys PKI Kits component
- Cost-effective scalability in a wide range of operational environments, including Windows, Linux, Solaris, Unix and AIX, etc
- Support X509 Certificate chain validation and PKCS#7 Signed Data validation
- Fully integrated with Jrsys 3A Secure Single Sign On system